NAM321/6 (50 ov)
 IRE
 GMB
 ZMB
 NGA
 LES
 CAG
 BOL
 COMO
 SAS
 FCA
 FCU
 KOE
 S04
 M05
 SVW
 RBL
 ELV
 MOZ19
 UGA23/0 (0.5/20 ov, target 20)
 NZ180/5
 IND181/6 (19.5/20 ov, target 181)
 Ipswich1
 Nottm Forest1
 Alavés1
 Málaga1
 WA105/3 (18.5/50 ov, target 372)
 NSW371/8
 DEN
 KUW
 KENYA
 QAT
 SWD-W
 EPR-W
 TTN-W
 WPR-W
 BOR
 WAR15/1 (2.5/20 ov)
 LIONS
 Limpo21/1 (2.5/20 ov)
 NZ-A135/3 (41 ov)
 IND-A113
 DHA293/3 (84.1 ov)
 RAJ
 MYMS
 CHATT
 RAN320/5 (80 ov)
 BAR
 MEX-W
 ARG-W
 UAE
 NED
 PAK
 ENG
 IND-W
 ZIM-W
 AFG170/3 (34.3/50 ov, target 170)
 ZIM169
 SCP
 HSV
 ARS
 EVE
 Torino3
 Monza2
 Brest1
 Nice2
 Stuttgart2
 Gladbach3
 Al Ahli4
 Al Khaleej1

Rust Security Stack Integration: Microsoft’s Security Response Center has long attributed roughly 70% of the CVEs it patches to memory-safety flaws — a figure the company has cited repeatedly in its public engineering posts.
That single statistic is why Rust, a language designed to eliminate entire classes of memory bugs at compile time, keeps appearing on enterprise security roadmaps. The question is no longer whether to adopt Rust, but how to connect it to your existing security model stack without breaking what already works.
Here’s the takeaway: you do not need a full rewrite. The practical path is incremental integration, where Rust takes over the security-critical functions while your legacy code stays in production.
Whether your stack is built on Python, Java, or C, this guide lays out the integration points, the trade-offs, and the timeline you should plan for.
Why Rust Belongs in Your Security Stack
Rust’s ownership model prevents use-after-free, double-free, and buffer overflows before code ever ships. Where C relies on developer discipline and runtime tools like AddressSanitizer, Rust enforces memory rules at compile time.
Worth noting: Google’s Chromium project has also reported that around 70% of its serious security bugs were memory-safety issues, per its own public security write-ups. Rust does not merely detect that category of bug at runtime — it rejects the code during compilation.
For security teams, that shifts effort from triage to prevention, which is a more durable use of engineering time.
Integration Approaches: FFI and Risk Boundaries
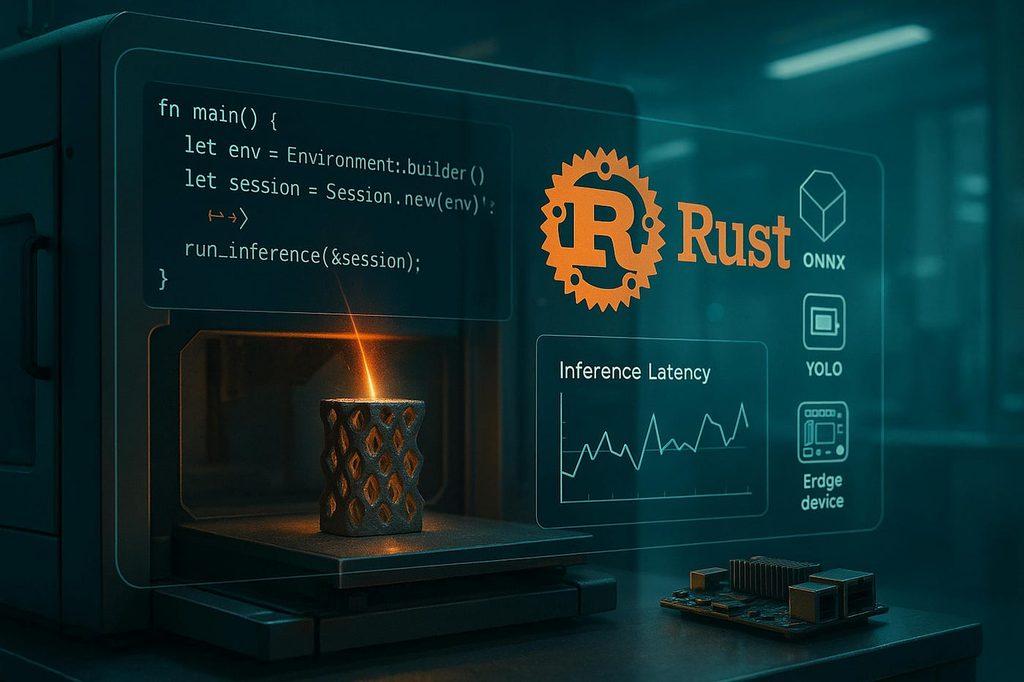
The most common path is the Foreign Function Interface, or FFI, which lets Rust libraries speak to C, C++, Python (via PyO3), and Java (via JNI). You keep the legacy codebase intact, but move security-critical functions — parsers, cryptographic operations, input validation — into Rust modules.
The boundary between languages becomes the new risk surface, so it deserves explicit design attention.
| Stack Layer | Typical Rust Role | Legacy Role |
|---|---|---|
| Parsing | Untrusted input handling | Orchestration |
| Crypto | Key management, signing | Key distribution |
| Network | TLS termination helpers | Connection pooling |
| Auth | Token validation | Session management |
The table shows a practical split. You do not port everything; you port the paths that touch untrusted data first, because that is where memory-safety bugs actually enter the system. As we covered in our security patch analysis, the highest-value fixes are almost always in input-facing code.
Performance and Memory Trade-offs
Adopting Rust is widely cited as a way to cut memory overhead. Because it has no garbage collector, Rust avoids the stop-the-world pauses that can affect managed runtimes under load.
For security tooling that processes high-throughput traffic, that can translate into lower latency per request and more predictable peak behaviour. That said, the integration cost is real. Your team must learn the borrow-checker rules, and FFI boundaries require careful handling of unsafe blocks.
The consensus practice is to keep unsafe code isolated, heavily reviewed, and confined to thin wrapper functions so that the rest of the codebase retains Rust’s guarantees. Skipping this discipline turns the integration into a new vulnerability source.
What’s Next: Tooling and adoption
Tooling has matured considerably. Cargo, Rust’s build system, now offers strong support for cross-compilation and reproducible builds, both of which matter for supply-chain security. The 2026 edition continues to expand the standard library, and crates like ring and clap are widely used in production security tools, per the official Rust ecosystem documentation.
For teams in India and globally, the practical next step is a pilot: pick one parser or one validation function, wrap it in Rust, and measure the change in crash reports and memory usage over a quarter. If the numbers hold, expand to the next untrusted-input path. Verdict: Start small, target untrusted input, and keep unsafe blocks isolated — that sequence delivers most of the memory-safety benefit with a fraction of the migration risk.
Related Articles
FAQs
Is Rust a drop-in replacement for my entire security stack?
No, and it should not be treated as one. Rust replaces the memory-unsafe core of your stack, while orchestration and business logic can remain in your existing language. Does integ No. The FFI approach lets you wrap existing C, C++, Python, or Java code and call Rust libraries from it, so you migrate only security-critical paths.
What are the main risks of FFI integration? The primary risks are unsafe blocks, data marshalling errors, and increased build complexity. Mitigate them by isolating unsafe code, adding fuzz tests at the boundary, and reviewing every unsafe block. How does Rust compare to Go for security tooling? Rust offers stronger compile-time memory guarantees, while Go offers faster onboarding and simpler concurrency. Choose Rust when memory safety is non-negotiable, and Go when team velocity matters more.
Was this article helpful?
Your feedback directly improves future articles on this site.