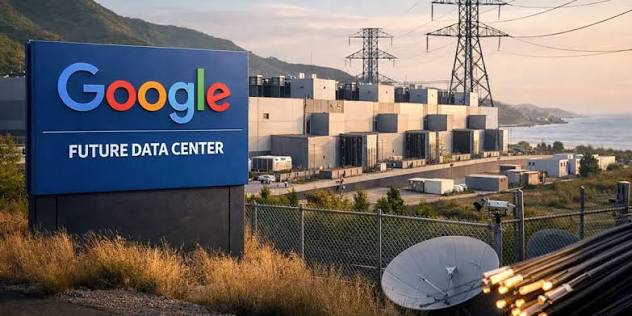
On Tuesday, October 6, 2026, Google, JPMorgan Chase, and two unnamed governments coordinated a patch for a shared vulnerability in the Model Context Protocol. The coordinated fix arrived via an industry-wide security update that remediated the critical routing bypass across multiple financial and cloud infrastructure stacks.
Until recently, enterprise AI integrations operated on isolated network segments, leaving foundational protocols exposed to independent exploitation attempts. When regulators finally approves data center-specific compliance frameworks last month, organizations assumed their internal model routing would remain completely insulated from external threats.

How The Vulnerability Exposed Legacy Routing Architecture
The original architecture allowed unverified context payloads to traverse secure API gateways without triggering standard authentication checks. Attack vectors targeting large language model deployments could inject malicious parameters directly into training loops or inference pipelines.
Financial institutions relying on real-time transaction forecasting faced immediate exposure when those payloads altered weighting algorithms. Cloud providers hosting enterprise workloads experienced identical failure modes during routine load balancing tests. Engineers discovered that the flaw stemmed from outdated handshake routines that prioritized speed over cryptographic verification. Malicious actors exploited this gap to redirect context streams through unmonitored proxy servers. The resulting data leakage forced immediate shutdowns across several major commercial platforms.
Why Cross-Industry Coordination Supports Policies That Approves Data Center-Specific Governance
Regulatory pressure accelerated the timeline after recent infrastructure audits revealed overlapping dependency chains. Teams managing massive computational clusters noted that isolated security patches consistently failed to address cross-platform handshake failures. Discussions around centralized governance gained traction following coverage of the ‘One Election Data framework proposed for regional server farms.
Industry leaders recognized that fragmented updates would leave critical pathways open during peak processing hours. The momentum shifted toward unified remediation after analysts highlighted how legacy hardware struggled under modern cryptographic demands. Similar concerns emerged when deployment strategies for mobile processors encountered thermal throttling bottlenecks during sustained workloads. A grassroots push regarding the Oregon Grassroots Data initiative further emphasized the need for standardized protocol enforcement across public and private networks. Joint development squads merged code repositories to ensure simultaneous rollout across competing ecosystems. For more detail, see Gizmodo.
Before Versus After The Coordinated Update
The patched environment now enforces strict payload validation before any context stream reaches the core inference engine. Authentication tokens require mutual verification between client endpoints and host servers, eliminating the previous trust-based handshake model.
Network traffic routing follows deterministic paths that prevent unauthorized parameter injection during high-volume query sessions. Compliance monitoring tools automatically flag deviations from the new baseline, triggering immediate isolation procedures for affected nodes. Administrators report significantly reduced false-positive alerts thanks to refined signature databases. Latency metrics remain stable despite the added cryptographic overhead. Enterprises transitioning to the new framework experience smoother migration workflows during off-peak maintenance windows.
| Component | Pre-Patch State | Post-Patch State |
|---|---|---|
| Authentication | Trust-based handshake | Mutual token verification |
| Payload Validation | Optional filtering | Strict mandatory inspection |
| Routing Paths | Dynamic and flexible | Deterministic and locked |
| Incident Response | Manual quarantine | Automated node isolation |
Where Enterprise Security Heads Next
Development teams will likely migrate toward zero-trust networking models to prevent similar coordination gaps. Hardware manufacturers are already integ
When enterprises finally approves data center-specific security mandates, they must align infrastructure upgrades with updated communication standards to maintain operational continuity. Choose deterministic routing for high-frequency trading systems, and select dynamic failover architectures for consumer-facing applications.
FAQs
What exactly was the vulnerability in the Model Context Protocol? The flaw allowed unverified context payloads to bypass standard authentication checks during API handshakes. This routing bypass enabled malicious parameter injection into active inference pipelines.
How quickly did the coordinated patch deploy across financial networks? The industry-wide security update rolled out simultaneously on Tuesday, October 6, 2026. Cloud providers and banking infrastructure received synchronized notification and installation windows. Will older hardware models receive compatibility support for the new encryption standards? Manufacturers are integ
Source: Thenextweb
Was this article helpful?
Your feedback directly improves future articles on this site.