MEX-W
 ARG-W
 CLB4
 TOR2
 Palmeiras1
 Bragantino0
 Vasco0
 Corinthians0
 UAE
 NED
 PAK
 ENG
 IND-W
 ZIM-W
 GMB
 LES
 MOZ
 ZMB
 Inter Milan
 Fiorentina
 Churchill
 Punjab FC
 NGA
 UGA
 ATM1
 DEP0
 LAZ2
 PAR1
 RCL2
 PAR1
 RIY2
 TAA1
 NZ-A135/3 (41 ov)
 IND-A113
 SYL
 KHU
 MYMS299/4 (87 ov)
 CHATT
 DHA293/3 (84.1 ov)
 RAJ
 RAN320/5 (80 ov)
 BAR
 DEN
 PNG
 NAM321/6
 IRE290 (47.3/50 ov, target 322)
 NZ180/5
 IND181/6 (19.5/20 ov, target 181)
 Athletic
 Getafe
 C Palace
 Newcastle
 Hull
 Brentford
 Liverpool
 Brighton
 Man United
 Bournemouth
 Atalanta
 Frosinone
 CHE0
 TOT2
 VAL1
 VIL2
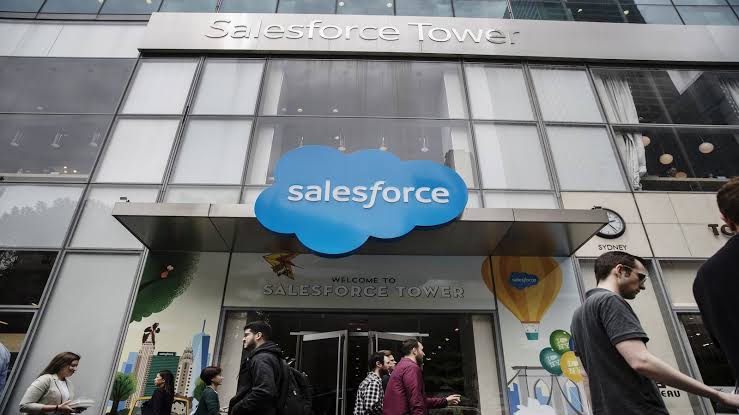
On Wednesday, September 30, 2026, industry reports described a single malicious or erroneous AI prompt causing a catastrophic failure inside a company’s Salesforce database. The incident was not independently confirmed by Salesforce or the affected company, and the available details are based on leaks and supply-chain reports that have not been officially confirmed.
Salesforce Sales Cloud Unlimited pricing starts at approximately $300 per user per month as of late 2026, making the reported failure a costly reminder that premium software can still depend on fragile automation. A blank screen is rarely the whole story. Behind it may be damaged records, broken permissions, failed workflows, and customer histories that no longer match the company’s live operations.
One Bad Prompt Took Down a Company’s Salesforce: The Reported Incident
The central claim is that one AI-generated instruction reached an enterprise Salesforce environment with enough authority to alter or damage critical database structures. The prompt may have been malicious, or it may have been an erroneous instruction interpreted by an automated agent. The available reports do not identify the company, the exact prompt, the affected Salesforce edition, or the scale of the data loss.
> “A single prompt became an enterprise control problem.” That distinction matters because the failure was not simply a chatbot producing a wrong answer. An AI agent connected to Salesforce can potentially read customer records, update fields, create tasks, trigger workflows, and call external services through application programming interfaces. If access controls are weak, a natural-language request can become an operational command. The immediate response would require isolating the integration, stopping automated jobs, and checking audit logs before restoring data. Every minute matters when sales teams, support agents, and finance departments use the same customer relationship management (CRM) records.
How AI Agents Can Damage Salesforce
Modern enterprise integrations commonly connect Salesforce to large language models such as OpenAI‘s GPT-4o or Anthropic’s Claude 3.5 Sonnet through secure application programming interface (API) endpoints. The model does not need direct database access to create risk; an agent can use approved tools that execute Salesforce actions after interpreting a prompt. Here’s the thing: “secure API” does not automatically mean safe automation.
A valid token with excessive permissions can allow an agent to make legitimate-looking changes at dangerous speed. Prompt injection, ambiguous instructions, poorly designed tool descriptions, or missing approval gates can turn a routine task into a destructive sequence. Cloud dependency adds another layer. Salesforce operations and CRM infrastructure rely on underlying cloud compute architectures typically hosted on Amazon Web Services or Microsoft Azure, so a failure can involve the Salesforce application, the AI integration, identity services, or the wider hosting path. Our earlier coverage of Prompt Caching, Explained is relevant here because cached instructions and reused context can increase the chance that an outdated or unsafe command is carried into a later workflow. For more detail, see VentureBeat AI.
Why the Company Could Face a Long Recovery
Database corruption is harder to repair than a temporary service outage. Engineers must determine which records changed, identify the last trusted state, preserve evidence, and prevent the same automation from rewriting restored data. Enterprise recovery often depends on automated backup products such as OwnBackup, now ope$300 per user each month for Sales Cloud Unlimited may still face lost selling time, delayed support, compliance reviews, and manual reconciliation across departments.
Enterprise AI Safeguards After the Salesforce Failure
The next investigation should focus on permissions, approval gates, and the exact chain between the prompt and the database action. Salesforce administrators will need to review API tokens, agent tools, audit trails, sandbox testing, and rules that prevent bulk updates without human approval. The reported failure also gives companies a clear design test: an AI agent should not be able to delete or rewrite production data merely because a prompt sounds confident.
Read-only access, narrow tool permissions, rate limits, staged deployment, and immutable backups can reduce the blast radius. If the incident is confirmed, it will move the debate from whether AI agents can work inside CRM systems to whether companies can prove what those agents did. That answer must come from logs, controls, and recoverable data—not from the model’s explanation after the damage is done. The lesson from the reported Salesforce failure is simple: enterprise AI needs a brake pedal before it receives a key. It is worth watching how One Bad Prompt Took Down develops from here.
FAQs
What happened in the Salesforce incident?
Industry reports on September 30, 2026, described a malicious or erroneous AI prompt causing a catastrophic failure inside a company’s Salesforce database. The affected company, exact prompt, and technical scope were not identified.
Was the incident officially confirmed?
No. Salesforce and the affected company had not officially confirmed the reported incident in the available information.
Which AI models can connect to Salesforce?
Enterprise integrations commonly use models such as OpenAI’s GPT-4o and Anthropic’s Claude 3.5 Sonnet through API endpoints. The specific model involved in this case is unknown.
How can a company recover corrupted CRM data?
Recovery may involve audit-log analysis and backups from services such as OwnBackup, now Own Company, or Druva. Restoration must also account for workflows and external systems changed after the corruption began.
What is the safest AI-agent setup?
A safer setup uses read-only permissions by default, limited tools, sandbox testing, approval gates for bulk changes, and immutable production backups.
Was this article helpful?
Your feedback directly improves future articles on this site.